

Apache Jackrabbit Overview
Apache Jackrabbit is a fully conforming implementation of the Content Repository for Java Technology API. It provides a robust content repository solution.
Use Cases
Customers recommend Content Management, Generation Of New Leads, Sending & Publishing Communications, as the business use cases that they have been most satisfied with while using Apache Jackrabbit.
Apache Jackrabbit Use-Cases and Business Priorities: Customer Satisfaction Data
Reviews
"...The business problems are to create the marketing content for business development...." Peer review by User
Peer review evidence (same sources as the product rating summary)
"...One of our main tools at the newspaper is AEM; this is an Adobe product based on several open source projects (Apache Sling, Apache Felix, Apache Jackrabbit), combining them in order to offer a nice content manager experience...." Touch UI: migrating to Adobe Experience Manager s new look
"...In combination with additional, independent authentication mechanisms, this may lead to the new password being disclosed...." Welcome to Apache Jackrabbit
"...Last Published: 2020-06-08. ..." Welcome to Apache Jackrabbit
Apache Jackrabbit, belong to a category of solutions that help Content Management Systems. Each of them excels in different abilities. Therefore, determining the best platform for your business will depend on your specific needs and requirements.
Apache Jackrabbit Customer wins, Customer success stories, Case studies
How efficiently Does Apache Jackrabbit manage your Content Management?
11 buyers and buying teams have used Cuspera to assess how well Apache Jackrabbit solved their Content Management Systems needs. Cuspera uses 135 insights from these buyers along with peer reviews, customer case studies, testimonials, expert blogs and vendor provided installation data to help you assess the fit for your specific Content Management Systems needs.
Apache Jackrabbit Features
- Low
- Medium
- High
| FEATURE | RATINGS AND REVIEWS |
|---|---|
| AI Powered | Read Reviews (1) |
| Custom Reports | Read Reviews (15) |
| Analytics | Read Reviews (4) |
| CAPABILITIES | RATINGS AND REVIEWS |
|---|---|
| AI Powered | Read Reviews (1) |
| Custom Reports | Read Reviews (15) |
| Analytics | Read Reviews (4) |
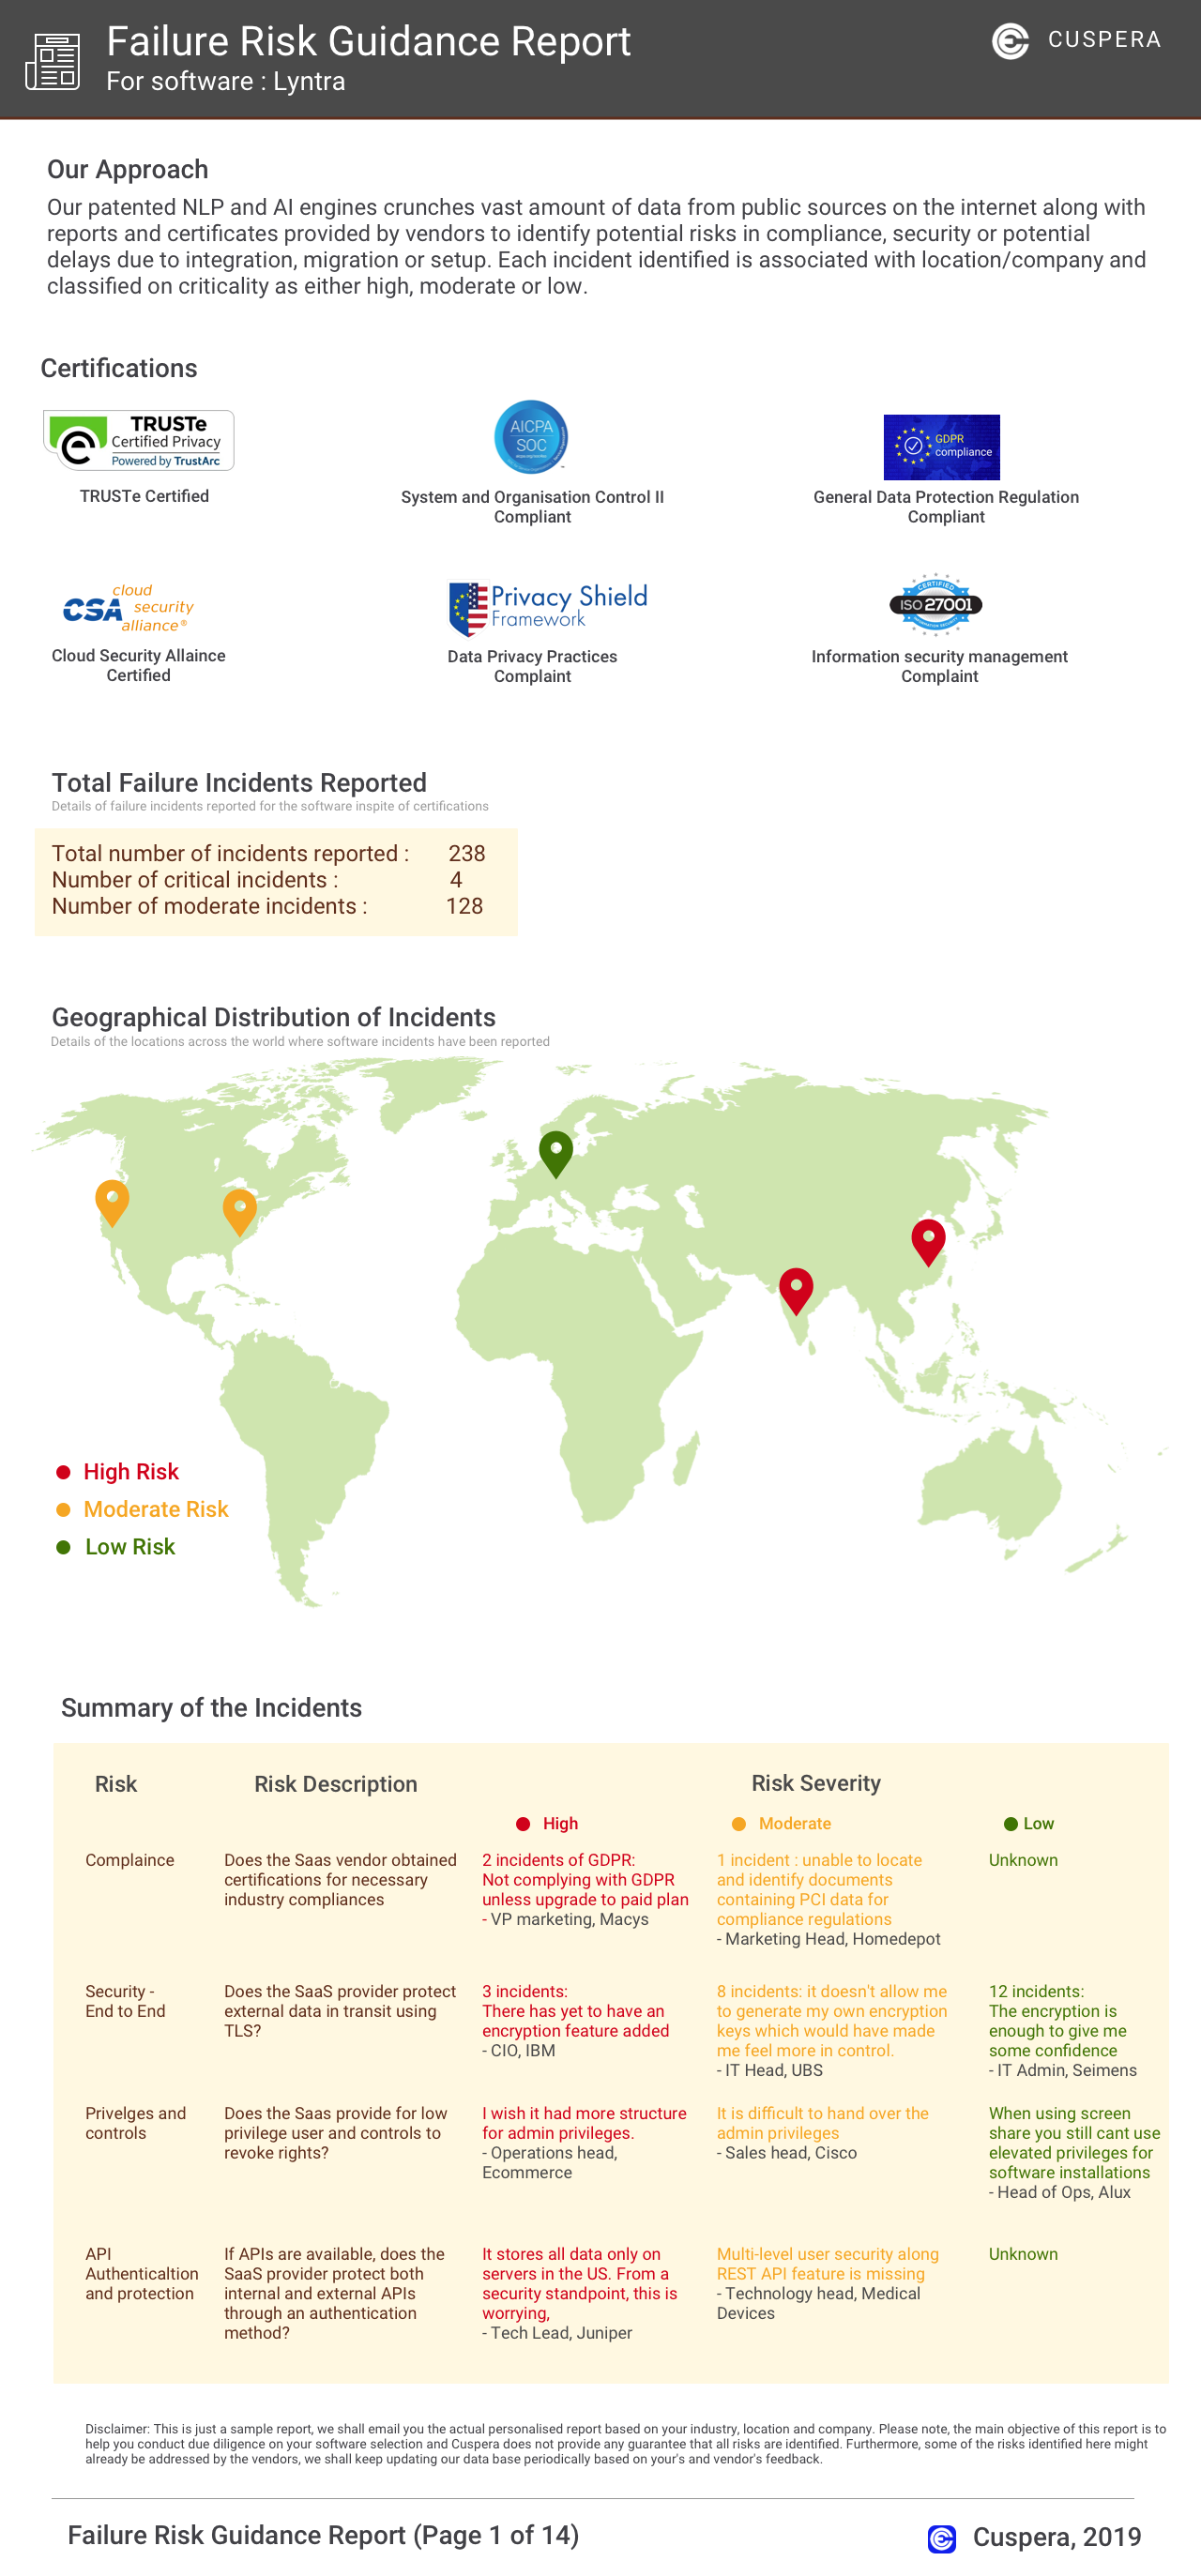
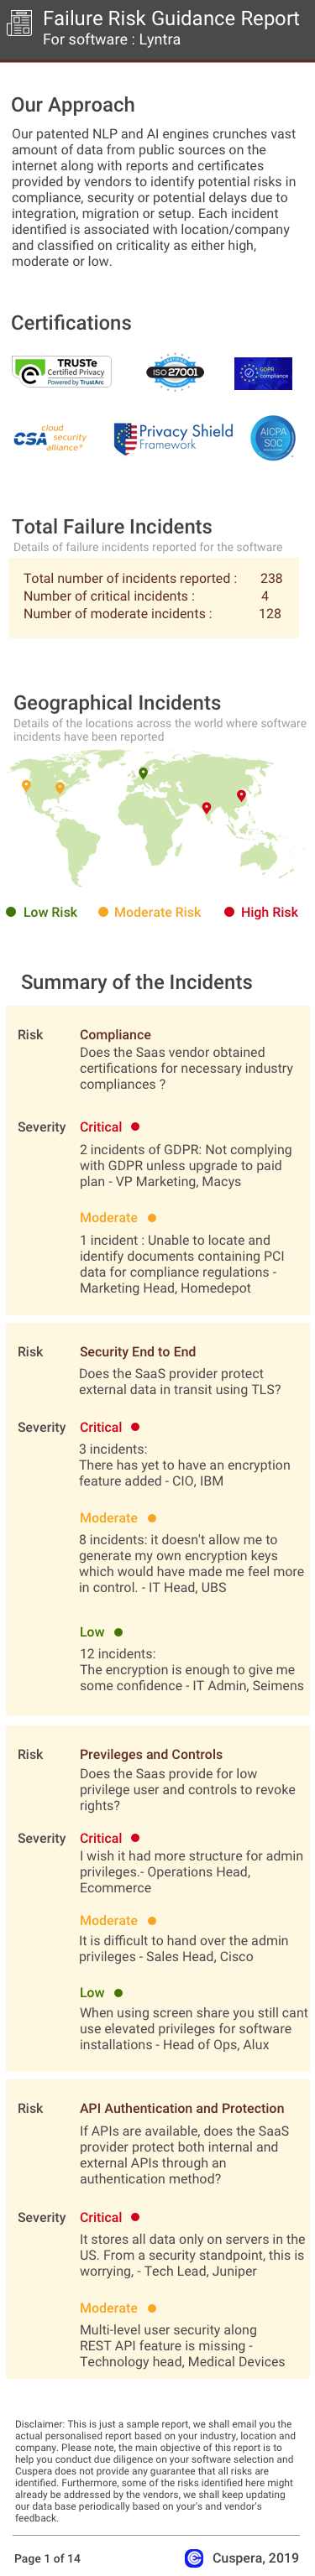
Software Failure Risk Guidance
?for Apache Jackrabbit
Top Failure Risks for Apache Jackrabbit
The Apache Software Foundation. News
CISA Warns of Apache Tomcat Encryption Vulnerability Actively Exploited ...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has identified a high-severity encryption vulnerability, CVE-2026-34486, in Apache Tomcat, urging organizations to apply fixes. The flaw affects versions 11.0.20, 10.1.53, and 9.0.116, with patches available in subsequent releases. This vulnerability allows attackers to bypass encryption, posing risks to clustered Tomcat deployments. Organizations are advised to upgrade immediately to mitigate potential exploitation.
Apache NiFi Vulnerabilities Enables Authorization Bypass Attacks
Apache has released NiFi version 2.11.0 to address multiple security vulnerabilities, including authorization bypass and memory exhaustion issues. The update enhances authorization checks and modifies request handling to prevent potential exploits. Users are advised to upgrade to mitigate risks associated with these vulnerabilities.
Warning: Multiple vulnerabilities in Apache Traffic Server, Patch ...
Apache Traffic Server has multiple vulnerabilities affecting versions 9.0.0 to 9.2.14 and 10.0.0 to 10.1.3. These include HTTP request smuggling and resource exhaustion. Apache advises upgrading to versions 9.2.15 or 10.1.4 to mitigate risks. The vulnerabilities are remotely exploitable and require no user interaction, posing significant security threats.
PoC Exploit Released for HTTP/2 Bomb Remote DoS Vulnerability in Apache ...
A PoC exploit for a critical DoS vulnerability in Apache HTTP Server, CVE-2026-49975, has been released. The flaw affects versions 2.4.17 to 2.4.67 and allows attackers to exhaust server memory. Apache HTTP Server 2.4.68 and later versions have patched this vulnerability. Organizations are advised to upgrade immediately or disable HTTP/2 temporarily.
The Apache Software Foundation. Profile
Company Name
Company Website
http://www.apache.org/HQ Location
401 Edgewater Place, Suite 600, Wakefield, MA 01880, US
Employees
1-10
Social

Financials
PRIVATE