


Splunk Enterprise Overview
Splunk Enterprise allows users to search, analyze, and visualize data for actionable insights. A free trial is available for those interested.
Use Cases
Customers recommend Communication Management, Social Media Analytics, Workflow Management, as the business use cases that they have been most satisfied with while using Splunk Enterprise.
Business Priorities
Scale Best Practices and Enhance Customer Relationships are the most popular business priorities that customers and associates have achieved using Splunk Enterprise.
Splunk Enterprise Use-Cases and Business Priorities: Customer Satisfaction Data
Splunk Enterprise works with different mediums / channels such as E-Mail. Chat. and Slack.
Splunk Enterprise's features include Dashboard, Alerts: Popups & Notifications, Recording, etc. and Splunk Enterprise support capabilities include Chat Support, Phone Support, AI Powered, etc. also Splunk Enterprise analytics capabilities include Analytics, and Custom Reports.
Reviews
"...We have been a Splunk customer for five years, and their technology is now core to us and their training is part of our new hire and onboarding process for all new developers and operations professionals...." Peer review by Pete Webb, Vice President of Production Operations, Groupon
Peer review evidence (same sources as the product rating summary)
"...Splunk will publish the data by connecting to any different source systems and shown in the dashboard with all the trend...." Peer review by Jagadish M., Information Technology and Services
"...Recorded Future for Splunk identifies indicators with elevated risk levels by analyzing web reporting, threat lists, and our own novel methods...." Bringing Recorded Future for Splunk Into Focus
"...Machine learning and AI technologies will help provide guidance on where teams should focus their energy on optimizing the workflow as well as provide insights into fluctuations in performance and demand, Josh Atwell, a senior technology advocate at Splunk told The New Stack...." AIOps: Is DevOps Ready for an Infusion of Artificial Intelligence?
Splunk Enterprise, Tubular, Digital Pigeon, eLogger, Cerberus FTP Server, etc., all belong to a category of solutions that help Data Management Platform. Each of them excels in different abilities. Therefore, determining the best platform for your business will depend on your specific needs and requirements.
Popular Business Setting
for Splunk Enterprise
Top Industries
- Information Technology and Services
- Computer Software
- Internet
Popular in
- Large Enterprise
- Enterprise
- Mid Market
Splunk Enterprise is popular in Information Technology And Services, Computer Software, and Internet and is widely used by Large Enterprise, Enterprise, and Mid Market.
Splunk Enterprise Customer wins, Customer success stories, Case studies
How does Splunk Enterprise facilitate Communication Management?
How does Splunk Enterprise address your Workflow Management Challenges?
How efficiently Does Splunk Enterprise manage your Onboarding?
How efficiently Does Splunk Enterprise manage your Competitive Intelligence?
11 buyers and buying teams have used Cuspera to assess how well Splunk Enterprise solved their Data Management Platform needs. Cuspera uses 14677 insights from these buyers along with peer reviews, customer case studies, testimonials, expert blogs and vendor provided installation data to help you assess the fit for your specific Data Management Platform needs.
Transportation Security Administration (TSA) - Government - Very Large
TSA inks $46M contract to acquire Splunk SIEM Licenses, Maintenance & Support
Cloud Surfing: Entering a Resilient Cloud Era
Frequently Asked Questions (FAQ)
What buyers ask before choosing Splunk Enterprise
What is Splunk Enterprise?
Splunk Enterprise is a machine data management and analytics platform that aggregate, analyze and get answers from data with the help of machine learning and real-time visibility. It allows users to process and index most forms of data in their native format.
It captures, indexes and correlates real-time data in a searchable repository from which it can generate graphs, reports, alerts, dashboards and visualizations. It enables team members to detect system anomalies and perform data clustering to filter out corrupted data.
Key features include data visualization, performance metrics, data collection, real-time search, indexing, KPI tracking, reporting, and monitoring. It offers integration with various third-party platforms including Microsoft Excel, Tableau, Okta, Azure AD, CA SiteMinder, OneLogin, and Optimal IdM.
What is Splunk Enterprise used for?
What are the top features of Splunk Enterprise?
Who uses Splunk Enterprise?
What are Splunk Enterprise alternatives?
Where is Splunk Enterprise located?

Peers used Splunk Enterprise for communication management and social media analytics
Splunk Enterprise Competitors


Splunk Enterprise Features
- Low
- Medium
- High
| FEATURE | RATINGS AND REVIEWS |
|---|---|
| AI Powered | Read Reviews (119) |
| Analytics | Read Reviews (818) |
| Custom Reports | Read Reviews (2069) |
| CAPABILITIES | RATINGS AND REVIEWS |
|---|---|
| AI Powered | Read Reviews (119) |
| Analytics | Read Reviews (818) |
| Custom Reports | Read Reviews (2069) |
Splunk Enterprise Integrations
Splunk Enterprise integrates with a wide range of software applications through its robust data import and export capabilities.


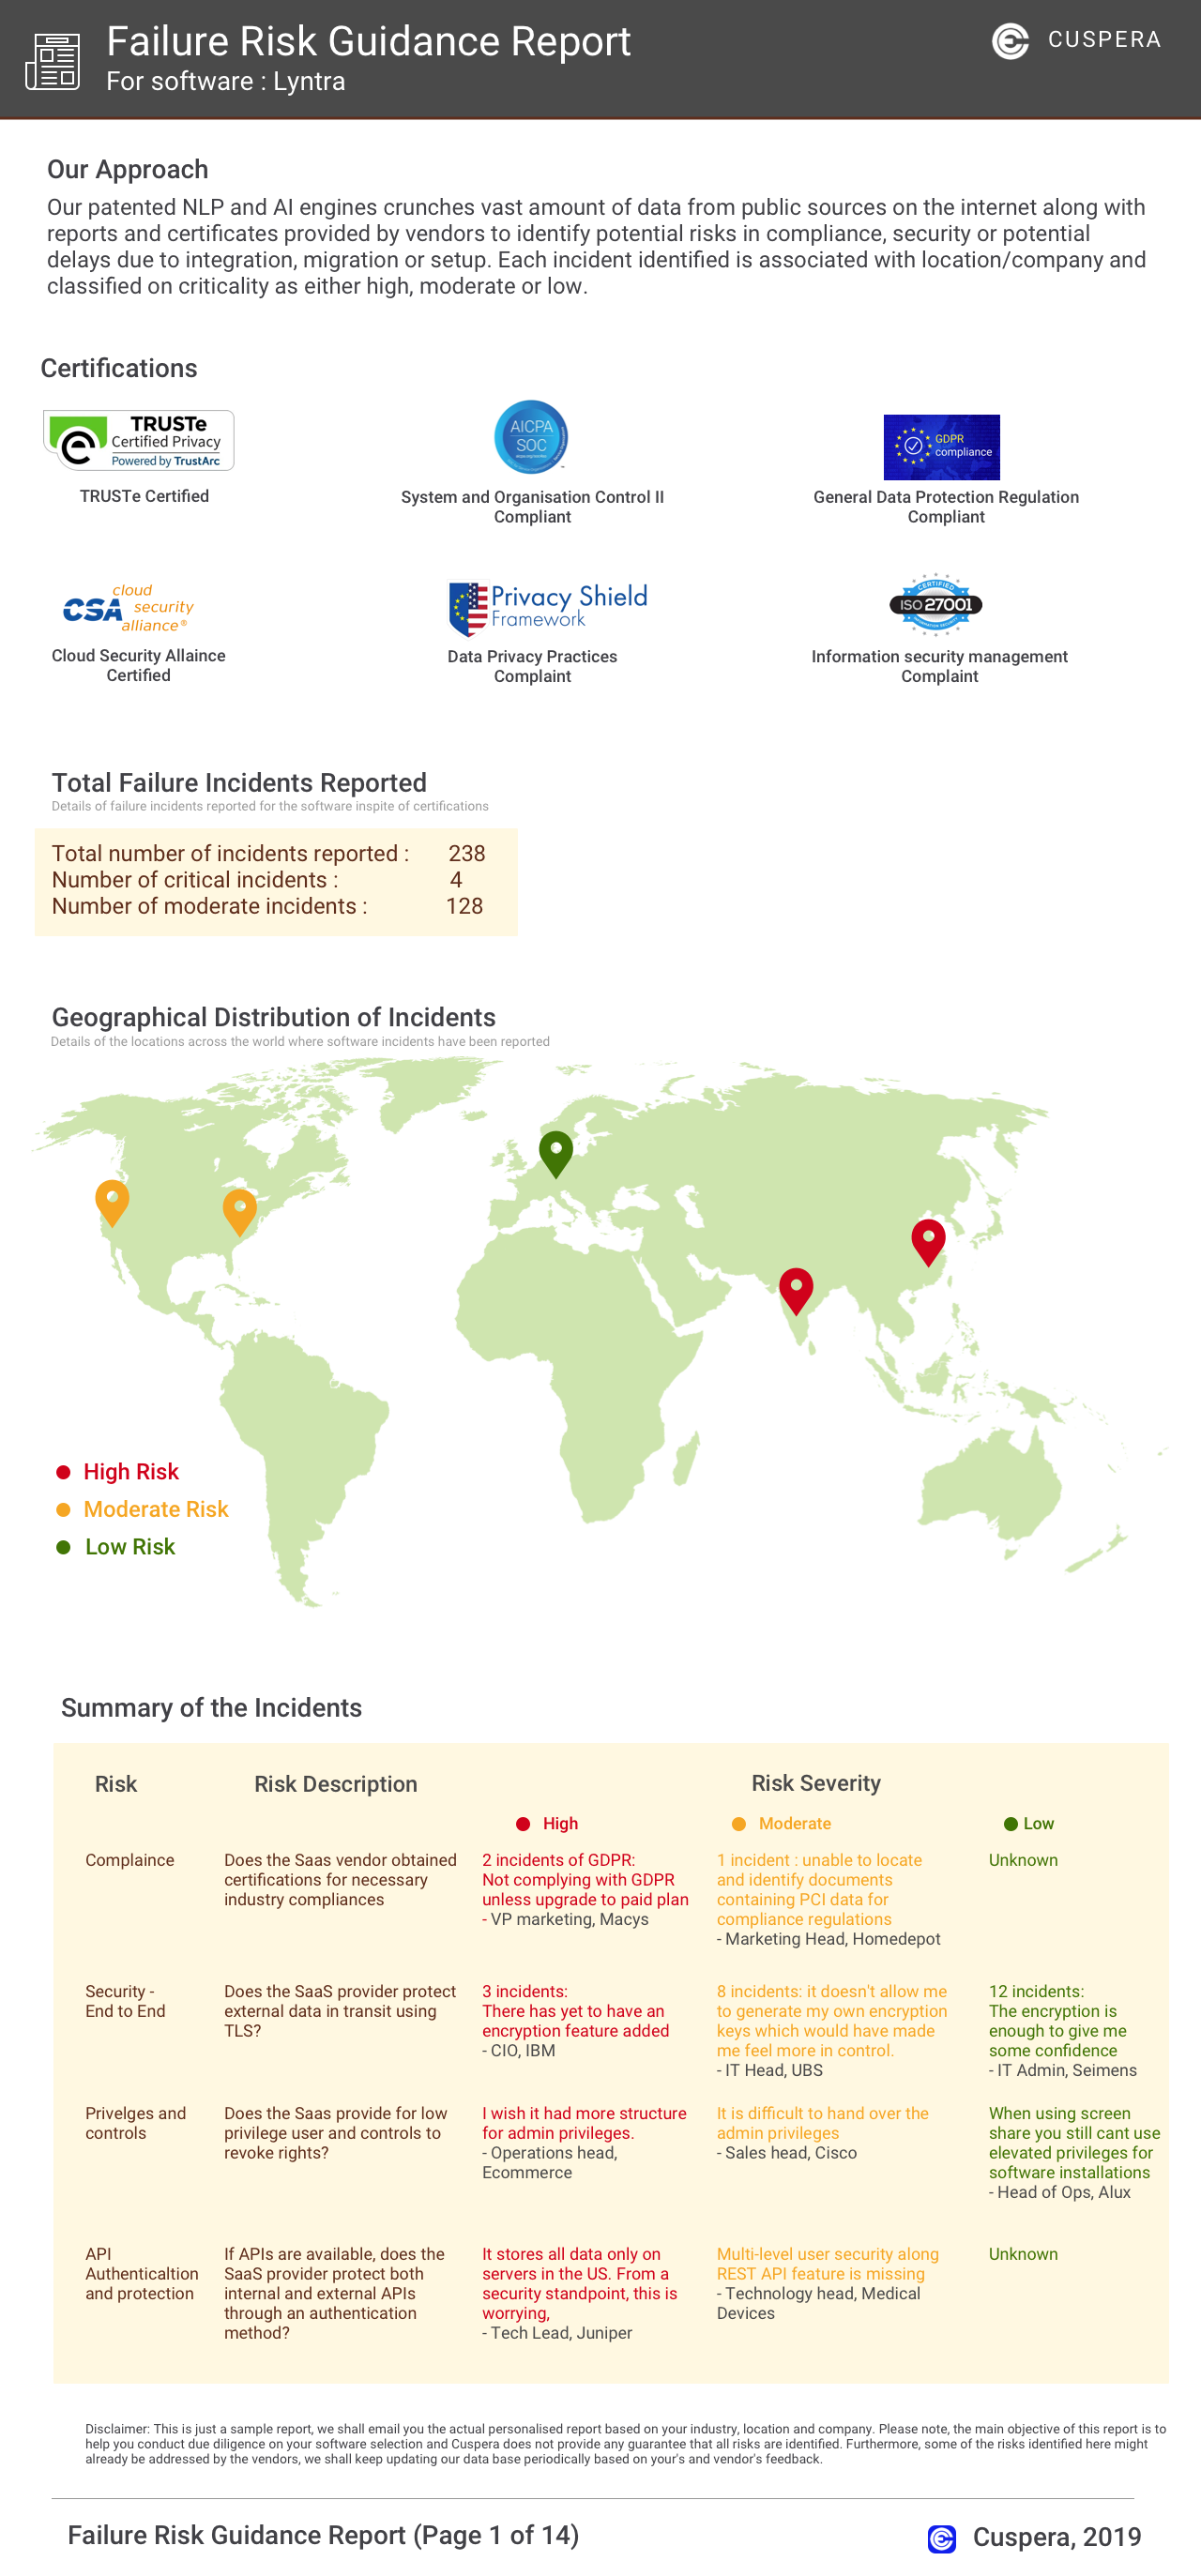
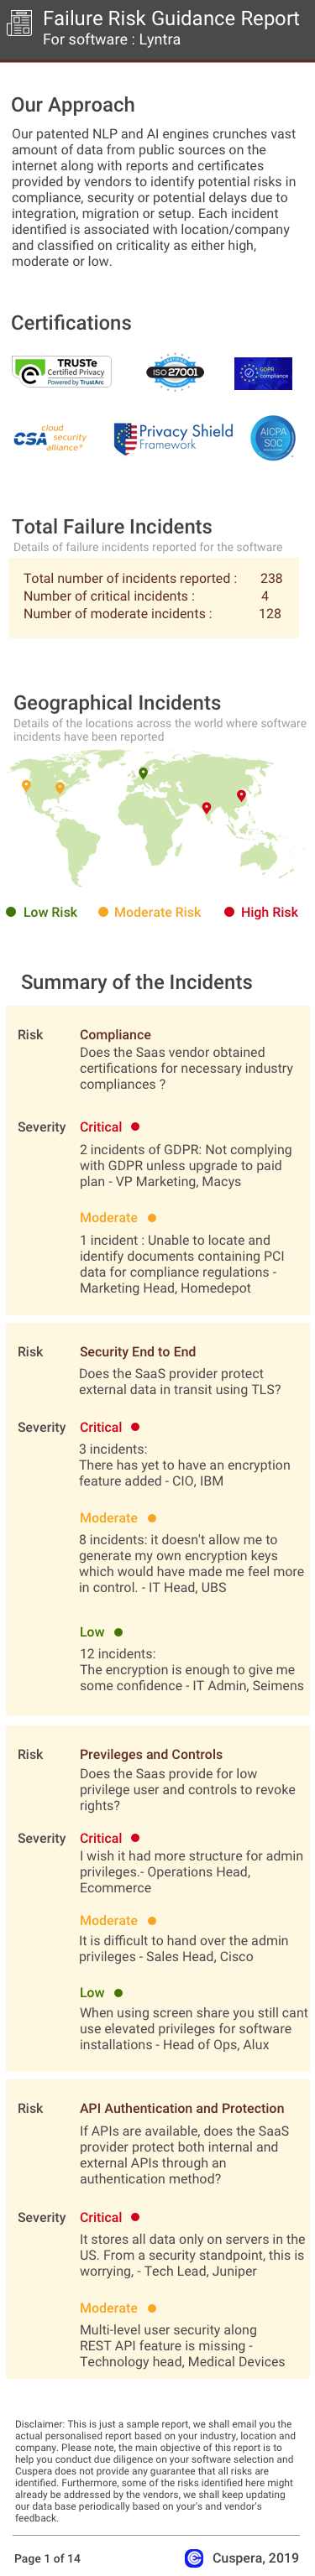
Software Failure Risk Guidance
?for Splunk Enterprise
Overall Risk Meter
Top Failure Risks for Splunk Enterprise
Splunk LLC News
SOCRadar Splunk Integration: New MSSP and Vulnerability Apps
SOCRadar has launched two new apps, SOCRadar Incidents MSSP and SOCRadar Vulnerability, on Splunkbase. These apps integrate with Splunk to provide multi-tenant security incident management and vulnerability assessment capabilities. The integration allows for streamlined data handling, tenant-safe data management, and direct alarm status updates within Splunk, enhancing security operations for managed service providers.
Warning: Multiple Vulnerabilities in Splunk Enterprise including critical RCE, Patch Immediately!
Splunk Enterprise is facing multiple vulnerabilities, including a critical remote code execution (RCE) flaw. Users are urged to patch immediately to mitigate potential security risks.
Splunk, Loom, ClearPass, SonicWall: Four Control Planes That Ship Without Auth
Splunk's cluster-coordination sidecar, among other products, was found to have a critical vulnerability (CVE-2026-76268) allowing unauthenticated access to configuration operations. The flaw, discovered internally, affects the Patroni REST API on search head cluster members. No active exploitation has been reported, and mitigation involves disabling the vulnerable component. This highlights a broader issue of missing authentication in critical functions across various platforms.
Splunk Products Multiple Vulnerabilities - Hong Kong Computer Emergency Response Team Coordination Centre
Multiple vulnerabilities have been identified in Splunk Enterprise versions 9.4 to 10.4, posing risks such as remote code execution and data manipulation. Users are advised to apply vendor-issued fixes to mitigate these security threats.
Splunk LLC Profile
Company Name
Company Website
https://www.splunk.com/HQ Location
270 Brannan St, San Francisco, California 94107, US
Employees
1001-5000
Social


Financials
IPO
How efficiently Does Splunk Enterprise manage your Social Media Analytics?